• Halloween is coming! To celebrate the occasion, we dusted off a couple of old skins, and even created a brand new one (Pixel).
    To get into the festive spirit, install the Skins extension.
  • The new Python extension is now available. It allows customers to deploy and manage WSGI-based Python applications on their websites directly from Plesk.
  • The Plesk Mobile apps for iOS and Android and the Plesk Mobile Center extension have been deprecated, and are no longer available for new installations. In Plesk Obsidian 18.0.84, the Plesk Mobile Center extension will be removed from servers during the upgrade, and the Plesk Mobile apps will lose their server management features.
  • The Social Login extension has been deprecated and will be removed in Plesk Obsidian 18.0.84. After that, it will no longer be possible to log in to Plesk with a Google, Facebook, GitHub account, or with a passkey. Plesk usernames and passwords, as well as logging in with a WebPros Account, are not affected.

Resolved Default plesk-wordpress fail2ban doesn't work

joemama

New Pleskian
Server operating system version
ubuntu 20.04
Plesk version and microupdate number
obsidian 18.0.50.2
filter:
[Definition]
failregex = ^<HOST>.* "POST .*/wp-login.php([/\?#\\].*)? HTTP/.*" 200
ignoreregex =

jail:
[plesk-wordpress]
enabled = true
filter = plesk-wordpress
action = iptables-multiport[name="wp-login", port="http,https", protocol="tcp"]
logpath = /var/www/vhosts/system/*/logs/*access*log
/var/log/apache2/*access.log
maxretry = 1

logs:
192.168.0.102 - - [27/Feb/2023:17:04:56 +0000] "POST /wp-login.php HTTP/1.0" 200 2886 "https://local.com/wp-login.php" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/103.0.0.0 Safari/537.36"
192.168.0.102 - - [27/Feb/2023:17:04:59 +0000] "POST /wp-login.php HTTP/1.0" 200 2885 "https://local.com/wp-login.php" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/103.0.0.0 Safari/537.36"

These are default values, i made sure fail2ban is enabled and that i am not in the white list, but anyways i don't get banned while bruteforcing wp-admin
 
You can to replace the regex from /etc/fail2ban/filter.d/plesk-wordpress.conf with
Code:
failregex = ^<HOST>.* "POST .*\/{0,}(.){0,}/wp-login\.php\?.* HTTP/.*" (200|503)
            ^<HOST>.* "POST .*\/{0,}(.){0,}/xmlrpc\.php HTTP\/.*" (200|302|503)
            ^<HOST>.* "POST .*\/{0,}(.){0,}/wp-login\.php HTTP\/.*" (200|503)
Don't forget to reload fail2ban or the wordpress login jail afterwards.
Does it improve the situation?
 
Thanks for your reply! Unfortunately it did not help.
In my situation the wordpress jail/filter is not triggered.

Here is some more information:
  • we have piped logs enabled
  • we see WARNINGS in fail2ban.log which might give a clue: Please check jail has possibly a timezone issue. Line with odd timestamp: domain.com:443 1.23.45.67 - - [12/Apr/2023:10:57:51 +0200]
  • we see lot's of xmlrpc requests in other_vhosts_access.log , for example:
Code:
domain.com:443 1.23.45.67 - - [12/Apr/2023:11:04:08 +0200] "POST //xmlrpc.php HTTP/1.0" 200 1345 "-" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36"
domain.com:443 1.23.45.67 - - [12/Apr/2023:11:04:09 +0200] "POST //xmlrpc.php HTTP/1.0" 200 1345 "-" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36"
domain.com:443 1.23.45.67 - - [12/Apr/2023:11:04:10 +0200] "POST //xmlrpc.php HTTP/1.0" 200 1345 "-" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36"


Code:
fail2ban-regex /var/log/apache2/other_vhosts_access.log /etc/fail2ban/filter.d/plesk-wordpress.local
Results
=======

Failregex: 36257 total
|-  #) [# of hits] regular expression
|   1) [36257] ^<HOST>.* "POST .*\/{0,}(.){0,}/xmlrpc\.php HTTP\/.*" (200|302|503)

plesk-wordpress jail
Code:
[plesk-wordpress]
enabled = true
filter = plesk-wordpress
action = iptables-allports[chain="INPUT", name="default", port="ssh", protocol="tcp", returntype="RETURN", lockingopt="-w"]
logpath = /var/log/apache2/other_vhosts_access.log
maxretry = 2

plesk-wordpress jail-filter
Code:
[Definition]
failregex = ^<HOST>.* "POST .*\/{0,}(.){0,}/xmlrpc\.php HTTP\/.*" (200|302|503)
ignoreregex =

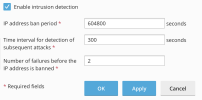
and from general fail2ban settings:
Schermafbeelding 2023-04-12 om 11.14.55.png

It seems the jail-filter is fine but for some reason the jail is not triggered.
 
Back
Top