• The new Python extension is now available. It allows customers to deploy and manage WSGI-based Python applications on their websites directly from Plesk.
  • The Plesk Mobile apps for iOS and Android and the Plesk Mobile Center extension have been deprecated, and are no longer available for new installations. In Plesk Obsidian 18.0.84, the Plesk Mobile Center extension will be removed from servers during the upgrade, and the Plesk Mobile apps will lose their server management features.
  • The Social Login extension has been deprecated and will be removed in Plesk Obsidian 18.0.84. After that, it will no longer be possible to log in to Plesk with a Google, Facebook, GitHub account, or with a passkey. Plesk usernames and passwords, as well as logging in with a WebPros Account, are not affected.

Question ETA for nginx 1.30.6 (Critical CVE-2026-15176, CVE-2026-93479, CVE-2026-97205)

DaMa

New Pleskian
Server operating system version
Almalinux
Plesk version and microupdate number
Plesk Obsidian 18.0.81 #4
Hi Plesk-Team,

when can we expect an update addressing the critical Nginx vulnerabilities CVE-2026-15176, CVE-2026-93479, and CVE-2026-97205 (CVSS 9.2)?

Thank you
 
Hi, @DaMa . Thank you for your question. Plesk Obsidian 18.0.82 already comes with Nginx 1.30.6, which is patched to the mentioned velnerabilities according to nginx security advisories

Our team is also working on a hotfix for Plesk Obsidian 18.0.81, which is likely going to be released today or on Monday.
 
Hi, @DaMa . Thank you for your question. Plesk Obsidian 18.0.82 already comes with Nginx 1.30.6, which is patched to the mentioned velnerabilities according to nginx security advisories

Our team is also working on a hotfix for Plesk Obsidian 18.0.81, which is likely going to be released today or on Monday.
Thanks for the information. However, as far as I can see, Plesk Obsidian 18.0.82 has not been released yet.
 
Hi, @DaMa . Thank you for your question. Plesk Obsidian 18.0.82 already comes with Nginx 1.30.6, which is patched to the mentioned velnerabilities according to nginx security advisories

Our team is also working on a hotfix for Plesk Obsidian 18.0.81, which is likely going to be released today or on Monday.
As soon as the hotfix goes live, please post it here so that anyone watching this thread receives a notification
 
It didn’t show up via the web UI update search, but did install via CLI. Is it supposed to be like this?
 
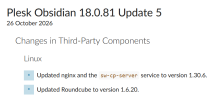
Make sure to restart sw-cp-server and nginx after the installation of the update. The update itself does not restart either, so you'll still run on the older version unless you restart both services.

Edit: I see that in some cases it tries to restart Nginx, but fails for whatever reason. This is not a big problem. However, in such cases you'll still need to restart manually.
 
Last edited:
Make sure to restart sw-cp-server and nginx after the installation of the update. The update itself does not restart either, so you'll still run on the older version unless you restart both services.

Edit: I see that in some cases it tries to restart Nginx, but fails for whatever reason. This is not a big problem. However, in such cases you'll still need to restart manually.
I looked in Tools & Settings > Assistance and Troubleshooting > Log Browser and sw-cp-server appears to have restarted itself showing active (running) since [minutes ago], (unless I'm mistaken?). Also this from SSH.

Code:
# sw-cp-serverd -v
nginx version: nginx/1.30.6

But my nginx did require a manual restart.

It didn’t show up via the web UI update search, but did install via CLI. Is it supposed to be like this?
I've experienced this too, but auto-update (if enabled) picks it up within 24 hours. However, like you, I have seen you can otherwise force an update sooner on the command line or by going into Tools & Settings > Plesk > Updates (opens a tab to port 8447) and it'll show Update Components as clickable where you'll find all the updates available to process.
 
Back
Top