• The new Python extension is now available. It allows customers to deploy and manage WSGI-based Python applications on their websites directly from Plesk.
  • Debian 11 has reached its end-of-life (vendor EOL date - August 31, 2026). Plesk Obsidian 18.0.81 is the last release to support it.
    If you are running Plesk Obsidian on Debian 11, we recommend you upgrade those servers to Debian 12 using our dist-upgrade tool.
  • We plan to deprecate and remove the support for XML RPC protocol versions earlier than 1.6.9.1 in Plesk Obsidian 18.0.82. We strongly recommend that you update all existing integrations using earlier versions of the XML RPC protocol to comply with the version 1.6.9.1 specification.

Resolved User role no longer able to change password

William Fong

New Pleskian
Server operating system version
AlmaLinux 8.10
Plesk version and microupdate number
Plesk Obsidian 18.0.80 #5
Dear Sir,

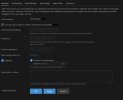
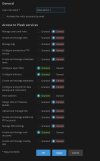
Just discover that under User Role, "Create and manage mail accounts" granted rights, it is no longer able to change user's password for existing users. That password portion has been grey off. We used to be able to do that in the past.

Could we have that feature back?

Thanks
 

Attachments

  • Screenshot 2026-08-28 122505.jpg
    Screenshot 2026-08-28 122505.jpg
    169.3 KB · Views: 13
Hi, @William Fong . I am afraid, I was unable to clearly understand the issue. Sorry. What password exactly are you looking forward to changing - the email account, the password of the user itself, or another one?

I configured a user role matching the permissions from the screenshot and I am able to change the email account permissions as well as adjust the password of the user. I would appreciate some further clarification.
Hi Sebahat, thank you for helping me out. Yes you got me right, I'm able to change to password for the same user that was logged in, but not for other users within the same domain. The password portion of the other users would be grey out.

Used to be able to do that in the past so that a user with the "Create and manage mail accounts" enabled role would help other users reset their passwords.
 

Attachments

  • Screenshot 2026-08-29 101346.jpg
    Screenshot 2026-08-29 101346.jpg
    155.5 KB · Views: 9
Thank you for the further clarification. I was able to replicate the behavior and opened an internal case for our team to confirm if that's a bug or expected behavior. I will follow up as soon as I get an update.
 
@William Fong , our team reviewed the case and confirmed that since Plesk Obsidian 18.0.80 this is intended behavior because a mail account that is also a Plesk login (i.e. associated with another user) shares one password, letting someone with only "Create and manage mail accounts" change it would let them log in to Plesk as the owner of that mailbox and inherit their permissions. Therefore, this path was closed as a security fix. The main point in that security fix is to limit the possibility for one additional user (e.g. test1) to be able to change the password and then log on behalf of the other user (e.g. test2). As a workaround, you can add the additional "Manage users and roles" permission to the created user role.
 
I have some concerns about the suggested workaround of granting the "Manage users and roles" permission.

I tested this workaround and found that a user who originally had only the "Create and manage mail accounts" permission could then modify their own user role and create additional users with permissions they were not originally granted.

Doesn't this introduce a potential privilege escalation issue, which seems to contradict the purpose of the security fix introduced in Plesk Obsidian 18.0.80?

I understand why users with only mail management permissions should not be allowed to change the passwords of other Plesk users who have administrative privileges. However, granting them the ability to manage users and roles seems to introduce a much broader security risk.

I also found that disabling "Can be used to log in to Plesk" does not remove the associated Plesk user, so the mail account password remains uneditable by the mail administrator.

However, deleting the associated Plesk user leaves the mail account intact and allows the mail administrator to change its password.

Wouldn't removing unnecessary Plesk users be a safer workaround for mail accounts that do not require Plesk access?

I would appreciate your thoughts on whether the suggested workaround is appropriate from a security perspective.
 
@Seiji Saiki , your concern is valid. If you grant the "Manage users and roles" permission users will be able to modify their own user role as well as other users'. Unfortunately, there's no other workaround we can suggest for allowing additional users the ability to change the passwords of email accounts that belong to other users.

Wouldn't removing unnecessary Plesk users be a safer workaround for mail accounts that do not require Plesk access?


That is a sound approach if the email address is associated with a user that's no longer being used. Once the user is removed the "Create and manage mail accounts" permission should be sufficient enough for you to change the password of the email account.
 
Thank you for your clarification and for confirming that removing unnecessary Plesk users is a valid approach.

I understand the current limitations.
I believe there is a legitimate need to allow users to manage only email accounts without granting them broader permissions to manage Plesk users and roles.
I hope a future Plesk update will provide a more flexible and secure way to handle this use case.

Thank you again for your help!
 
Back
Top